برنامج Hijackthis من اهم البرامج لمكافحة الحكر والفايرسات والبرامج الضاره وكل شي

متابعة النقاش، صفحة 8
شاركي في النقاش

سجلي الدخول لإضافة تعليق.

التعليقات

61
  1. @o2

    صاحبة الموضوع
    كنت بقول لك ان جهازك فيه فيروسات
    وانا قاعده ابحث لك عن برامج لتنظيفها لكن بجبلك برامج قويه وتنظف لك جهازك .. وتعرفي البحث في النت عن برامج شي متعب لكنه ممتع وانا استفيد


    http://securityresponse.symantec.com...r/FxSasser.exe


    بعدين ادخلي علي هالموقع واضغطي انستايل سكان

    http://www.liutilities.com/products/campaigns/affiliate/cb/offer/neuber/en/rb/


  2. Logfile of Trend Micro HijackThis v2.0.2
    Scan saved at 04:01:06 ص, on 04/02/11
    Platform: Unknown Windows (WinNT 6.01.3504)
    MSIE: Internet Explorer v8.00 (8.00.7600.16700)
    Boot mode: Normal
    Running processes:
    C:\Program Files (x86)\TOSHIBA\ConfigFree\NDSTray.exe
    C:\Program Files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe
    C:\Program Files (x86)\Internet Download Manager\IDMan.exe
    C:\Program Files (x86)\RocketDock\RocketDock.exe
    C:\Program Files (x86)\Toshiba\Bluetooth Toshiba Stack\TosBtMng.exe
    C:\Program Files (x86)\Intel\Intel(R) Rapid Storage Technology\IAStorIcon.exe
    C:\Program Files (x86)\Common Files\Real\Update_OB\realsched.exe
    C:\Program Files (x86)\Avira\AntiVir Desktop\avgnt.exe
    C:\Program Files (x86)\PC Tools Security\BDT\FGuard.exe
    C:\Program Files (x86)\Internet Download Manager\IEMonitor.exe
    C:\Program Files (x86)\TOSHIBA\ConfigFree\CFSwMgr.exe
    C:\Program Files\TOSHIBA\HDMICtrlMan\HCMSoundChanger.exe
    C:\Program Files (x86)\Toshiba\Bluetooth Toshiba Stack\TosA2dp.exe
    C:\Program Files (x86)\Toshiba\Bluetooth Toshiba Stack\TosBtHid.exe
    C:\Program Files (x86)\Toshiba\Bluetooth Toshiba Stack\TosBtHsp.exe
    C:\Program Files (x86)\Toshiba\Bluetooth Toshiba Stack\TosAVRC.exe
    C:\Program Files (x86)\Internet Explorer\iexplore.exe
    C:\Program Files (x86)\Internet Explorer\iexplore.exe
    C:\Program Files (x86)\Internet Explorer\iexplore.exe
    C:\Program Files (x86)\WinRAR\WinRAR.exe
    C:\Users\mohamed\AppData\Local\Temp\Rar$EX00.789\HijackThis.exe
    R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
    R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
    R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
    R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
    R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page = C:\Windows\SysWOW64\blank.htm
    R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
    R3 - URLSearchHook: (no name) - {28b716d8-f878-489c-9146-96d3288d7ecd} - (no file)
    R3 - URLSearchHook: (no name) - {a1e75a0e-4397-4ba8-bb50-e19fb66890f4} - (no file)
    R3 - URLSearchHook: PC Tools Browser Guard - {472734EA-242A-422b-ADF8-83D1E48CC825} - C:\Program Files (x86)\PC Tools Security\BDT\PCTBrowserDefender.dll
    O2 - BHO: IDM Helper - {0055C089-8582-441B-A0BF-17B458C2A3A8} - C:\Program Files (x86)\Internet Download Manager\IDMIECC.dll
    O2 - BHO: AcroIEHelperStub - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
    O2 - BHO: Browser Defender BHO - {2A0F3D1B-0909-4FF4-B272-609CCE6054E7} - C:\Program Files (x86)\PC Tools Security\BDT\PCTBrowserDefender.dll
    O2 - BHO: RealPlayer Download and Record Plugin for Internet Explorer - {3049C3E9-B461-4BC5-8870-4C09146192CA} - C:\ProgramData\Real\RealPlayer\BrowserRecordPlugin\IE\rpbrowserrecordplugin.dll
    O2 - BHO: مساعد تسجيل الدخول إلى Windows Live - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
    O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
    O2 - BHO: Google Toolbar Notifier BHO - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} - C:\Program Files (x86)\Google\GoogleToolbarNotifier\5.6.5805.1910\swg.dll
    O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files (x86)\Java\jre6\bin\jp2ssv.dll
    O3 - Toolbar: Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
    O3 - Toolbar: PC Tools Browser Guard - {472734EA-242A-422B-ADF8-83D1E48CC825} - C:\Program Files (x86)\PC Tools Security\BDT\PCTBrowserDefender.dll
    O4 - HKLM\..\Run: C:\Program Files (x86)\Intel\Intel(R) Rapid Storage Technology\IAStorIcon.exe
    O4 - HKLM\..\Run: %ProgramFiles%\TOSHIBA\Bluetooth Toshiba Stack\ItSecMng.exe /START
    O4 - HKLM\..\Run: %ProgramFiles(x86)%\TOSHIBA\TOSHIBA USB Sleep and Charge Utility\TUSBSleepChargeSrv.exe
    O4 - HKLM\..\Run: "C:\Program Files (x86)\TOSHIBA\TOSHIBA Web Camera Application\TWebCamera.exe" autorun
    O4 - HKLM\..\Run: "C:\Program Files (x86)\Common Files\Real\Update_OB\realsched.exe" -osboot
    O4 - HKLM\..\Run: "C:\Program Files (x86)\Adobe\Reader 9.0\Reader\Reader_sl.exe"
    O4 - HKLM\..\Run: "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
    O4 - HKLM\..\Run: "C:\Program Files (x86)\Malwarebytes' Anti-Malware\mbam.exe" /runcleanupscript
    O4 - HKLM\..\Run: "C:\Program Files (x86)\Avira\AntiVir Desktop\avgnt.exe" /min
    O4 - HKLM\..\Run: C:\Program Files (x86)\PC Tools Security\BDT\FGuard.exe
    O4 - HKCU\..\Run: "C:\Program Files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe"
    O4 - HKCU\..\Run: C:\Program Files (x86)\Internet Download Manager\IDMan.exe /onboot
    O4 - HKCU\..\Run: "C:\Program Files (x86)\RocketDock\RocketDock.exe"
    O4 - HKUS\S-1-5-18\..\Run: C:\Program Files (x86)\TOSHIBA\Toshiba Online Product Information\topi.exe (User 'SYSTEM')
    O4 - HKUS\.DEFAULT\..\Run: C:\Program Files (x86)\TOSHIBA\Toshiba Online Product Information\topi.exe (User 'Default user')
    O4 - .DEFAULT User Startup: TRDCReminder.lnk = C:\Program Files (x86)\TOSHIBA\TRDCReminder\TRDCReminder.exe (User 'Default user')
    O4 - Global Startup: Adobe Gamma Loader.lnk = C:\Program Files (x86)\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
    O4 - Global Startup: Bluetooth Manager.lnk = ?
    O8 - Extra context menu item: Add to AMV Convert Tool... - C:\Program Files (x86)\MP3 Player Utilities 4.00\AMVConverter\grab.html
    O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~2\MIF5BA~1\Office12\EXCEL.EXE/3000
    O8 - Extra context menu item: Google Sidewiki... - res://C:\Program Files (x86)\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_89D8574934B26AC4.dll/cmsidewiki.html
    O8 - Extra context menu item: Internet Download Manager تحميل بواسطة - C:\Program Files (x86)\Internet Download Manager\IEExt.htm
    O8 - Extra context menu item: MediaManager tool grab multimedia file - C:\Program Files (x86)\MP3 Player Utilities 4.00\MediaManager\grab.html
    O8 - Extra context menu item: ت&صدير إلى Microsoft Excel - res://C:\PROGRA~2\MIF5BA~1\Office12\EXCEL.EXE/3000
    O8 - Extra context menu item: تحميل الكل بواسطة Internet Download Manager - C:\Program Files (x86)\Internet Download Manager\IEGetAll.htm
    O8 - Extra context menu item: تحميل محتوى FLV بواسطة Internet Download Manager - C:\Program Files (x86)\Internet Download Manager\IEGetVL.htm
    O9 - Extra button: Send to OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~2\MIF5BA~1\Office12\ONBttnIE.dll
    O9 - Extra 'Tools' menuitem: S&end to OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~2\MIF5BA~1\Office12\ONBttnIE.dll
    O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~2\MIF5BA~1\Office12\REFIEBAR.DLL
    O16 - DPF: {6924091F-CD97-41E1-B1D4-D9079409D413} (IMCv1 Control) - http://74.81.167.185:1999/talk.cab
    O16 - DPF: {7253A666-804A-1107-A4DC-00E04C504780} (BMC Control) - http://www.ksacam.info/bmc.cab
    O16 - DPF: {7253A666-804A-1107-A4DC-00E04C504788} (BMC Control) - http://74.86.165.248/inc/bmc.cab
    O16 - DPF: {B7FDB0C3-4724-46D2-B8DB-6FA1DC63F7CA} (ReadUid.UserControlMacEntry) - http://74.81.167.185:1999/ReadUid.CAB
    O16 - DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} (Shockwave Flash Object) - http://fpdownload2.macromedia.com/get/shockwave/cabs/flash/swflash.cab
    O16 - DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7} - http://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab
    O23 - Service: @%SystemRoot%\system32\Alg.exe,-112 (ALG) - Unknown owner - C:\Windows\System32\alg.exe (file missing)
    O23 - Service: Avira AntiVir MailGuard (AntiVirMailService) - Avira GmbH - C:\Program Files (x86)\Avira\AntiVir Desktop\avmailc.exe
    O23 - Service: Avira AntiVir Scheduler (AntiVirSchedulerService) - Avira GmbH - C:\Program Files (x86)\Avira\AntiVir Desktop\sched.exe
    O23 - Service: Avira AntiVir Guard (AntiVirService) - Avira GmbH - C:\Program Files (x86)\Avira\AntiVir Desktop\avguard.exe
    O23 - Service: Avira AntiVir WebGuard (AntiVirWebService) - Avira GmbH - C:\Program Files (x86)\Avira\AntiVir Desktop\AVWEBGRD.EXE
    O23 - Service: BandLuxe Service (BandLuxe_Service) - BandRich Inc. - C:\Program Files (x86)\BandRich\BandLuxe HSDPA Utility R11\BRService.exe
    O23 - Service: Browser Defender Update Service - Threat Expert Ltd. - C:\Program Files (x86)\PC Tools Security\BDT\BDTUpdateService.exe
    O23 - Service: ConfigFree WiMAX Service (cfWiMAXService) - TOSHIBA CORPORATION - C:\Program Files (x86)\TOSHIBA\ConfigFree\CFIWmxSvcs64.exe
    O23 - Service: ConfigFree Service - TOSHIBA CORPORATION - C:\Program Files (x86)\TOSHIBA\ConfigFree\CFSvcs.exe
    O23 - Service: Defragmentation-Service (DfSdkS) - mst software GmbH, Germany - C:\Program Files (x86)\Ashampoo\Ashampoo WinOptimizer 2010 Advanced\Dfsdks.exe
    O23 - Service: @%SystemRoot%\system32\efssvc.dll,-100 (EFS) - Unknown owner - C:\Windows\System32\lsass.exe (file missing)
    O23 - Service: FABS - Helping agent for MAGIX media database (Fabs) - MAGIX AG - C:\Program Files (x86)\Common Files\MAGIX Services\Database\bin\FABS.exe
    O23 - Service: @%systemroot%\system32\fxsresm.dll,-118 (Fax) - Unknown owner - C:\Windows\system32\fxssvc.exe (file missing)
    O23 - Service: Firebird Server - MAGIX Instance (FirebirdServerMAGIXInstance) - MAGIX® - C:\Program Files (x86)\Common Files\MAGIX Services\Database\bin\fbserver.exe
    O23 - Service: GameConsoleService - WildTangent, Inc. - C:\Program Files (x86)\TOSHIBA Games\TOSHIBA Game Console\GameConsoleService.exe
    O23 - Service: GFNEX Service (GFNEXSrv) - Unknown owner - C:\Windows\System32\GFNEXSrv.exe (file missing)
    O23 - Service: خدمة تحديث Google (gupdate) (gupdate) - Google Inc. - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
    O23 - Service: Google Software Updater (gusvc) - Google - C:\Program Files (x86)\Google\Common\Google Updater\GoogleUpdaterService.exe
    O23 - Service: Intel(R) Rapid Storage Technology (IAStorDataMgrSvc) - Intel Corporation - C:\Program Files (x86)\Intel\Intel(R) Rapid Storage Technology\IAStorDataMgrSvc.exe
    O23 - Service: @keyiso.dll,-100 (KeyIso) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
    O23 - Service: Intel(R) Management and Security Application Local Management Service (LMS) - Intel Corporation - C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\LMS\LMS.exe
    O23 - Service: @comres.dll,-2797 (MSDTC) - Unknown owner - C:\Windows\System32\msdtc.exe (file missing)
    O23 - Service: @%SystemRoot%\System32\netlogon.dll,-102 (Netlogon) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
    O23 - Service: NVIDIA Display Driver Service (nvsvc) - Unknown owner - C:\Windows\system32\nvvsvc.exe (file missing)
    O23 - Service: @%systemroot%\system32\psbase.dll,-300 (ProtectedStorage) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
    O23 - Service: @%systemroot%\system32\Locator.exe,-2 (RpcLocator) - Unknown owner - C:\Windows\system32\locator.exe (file missing)
    O23 - Service: @%SystemRoot%\system32\samsrv.dll,-1 (SamSs) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
    O23 - Service: @%SystemRoot%\system32\snmptrap.exe,-3 (SNMPTRAP) - Unknown owner - C:\Windows\System32\snmptrap.exe (file missing)
    O23 - Service: @%systemroot%\system32\spoolsv.exe,-1 (Spooler) - Unknown owner - C:\Windows\System32\spoolsv.exe (file missing)
    O23 - Service: @%SystemRoot%\system32\sppsvc.exe,-101 (sppsvc) - Unknown owner - C:\Windows\system32\sppsvc.exe (file missing)
    O23 - Service: Notebook Performance Tuning Service (TEMPRO) (TemproMonitoringService) - Toshiba Europe GmbH - C:\Program Files (x86)\Toshiba TEMPRO\TemproSvc.exe
    O23 - Service: TOSHIBA HDD Protection (Thpsrv) - Unknown owner - C:\Windows\system32\ThpSrv.exe (file missing)
    O23 - Service: TOSHIBA Optical Disc Drive Service (TODDSrv) - Unknown owner - C:\Windows\system32\TODDSrv.exe (file missing)
    O23 - Service: TOSHIBA Power Saver (TosCoSrv) - TOSHIBA Corporation - C:\Program Files\TOSHIBA\Power Saver\TosCoSrv.exe
    O23 - Service: TOSHIBA Bluetooth Service - TOSHIBA CORPORATION - C:\Program Files (x86)\Toshiba\Bluetooth Toshiba Stack\TosBtSrv.exe
    O23 - Service: TOSHIBA eco Utility Service - TOSHIBA Corporation - C:\Program Files\TOSHIBA\TECO\TecoService.exe
    O23 - Service: TPCH Service (TPCHSrv) - TOSHIBA Corporation - C:\Program Files\TOSHIBA\TPHM\TPCHSrv.exe
    O23 - Service: @%SystemRoot%\system32\ui0detect.exe,-101 (UI0Detect) - Unknown owner - C:\Windows\system32\UI0Detect.exe (file missing)
    O23 - Service: Intel(R) Management & Security Application User Notification Service (UNS) - Intel Corporation - C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\UNS\UNS.exe
    O23 - Service: @%SystemRoot%\system32\vaultsvc.dll,-1003 (VaultSvc) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
    O23 - Service: @%SystemRoot%\system32\vds.exe,-100 (vds) - Unknown owner - C:\Windows\System32\vds.exe (file missing)
    O23 - Service: @%systemroot%\system32\vssvc.exe,-102 (VSS) - Unknown owner - C:\Windows\system32\vssvc.exe (file missing)
    O23 - Service: @%SystemRoot%\system32\Wat\WatUX.exe,-601 (WatAdminSvc) - Unknown owner - C:\Windows\system32\Wat\WatAdminSvc.exe (file missing)
    O23 - Service: @%systemroot%\system32\wbengine.exe,-104 (wbengine) - Unknown owner - C:\Windows\system32\wbengine.exe (file missing)
    O23 - Service: @%Systemroot%\system32\wbem\wmiapsrv.exe,-110 (wmiApSrv) - Unknown owner - C:\Windows\system32\wbem\WmiApSrv.exe (file missing)
    O23 - Service: @%PROGRAMFILES%\Windows Media Player\wmpnetwk.exe,-101 (WMPNetworkSvc) - Unknown owner - C:\Program Files (x86)\Windows Media Player\wmpnetwk.exe (file missing)
    --
    End of file - 14331 bytes
  3. @o2

    صاحبة الموضوع
    ❤ عطريـﮯانفاسـﮭﮯ ❤
    Logfile of Trend Micro HijackThis v2.0.2 Scan saved at 04:01:06 ص, on 04/02/11 Platform: Unknown Windows (WinNT 6.01.3504) MSIE: Internet Explorer v8.00 (8.00.7600.16700) Boot mode: Normal Running processes: C:\Program Files (x86)\TOSHIBA\…
    O23 - Service: @%SystemRoot%\system32\vaultsv c.dll,-1003 (VaultSvc) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)

    O23 - Service: @%systemroot%\system32\psbase. dll,-300 (ProtectedStorage) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)

    O23 - Service: @%SystemRoot%\system32\samsrv. dll,-1 (SamSs) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)

    تحسن ملحوظ :27:

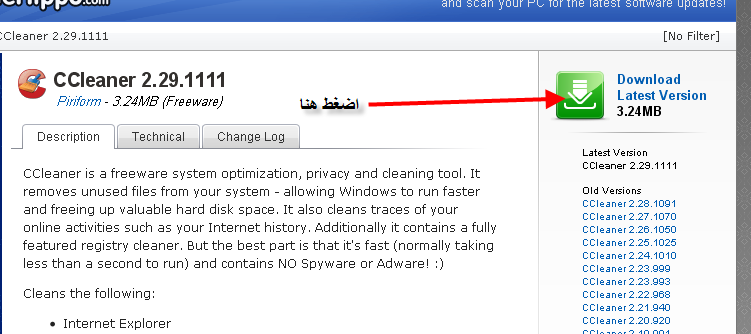
    امممم انصحك تركبي بررنامج ccleaner
    http://www.filehippo.com/download_ccleaner/

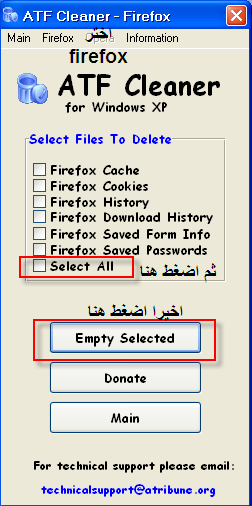
    عد تشغيل البرتامج حددي الكل بعلامة صح .. بعدين تحليل بعدين تنظيف

    وحملي هالبرنامج


    http://www.atribune.org/public-beta/ATF-Cleaner.exe


    وبكمل معاكي بكره

    وجيبي تقرير بعد كل ذا :27:

تابعي تجارب أخرى من هذا القسم.